My dude, do not track this file on a public github repo and purge it from git history: https://
github.com/BerriAI/litell
m/blob/main/.claude/settings.json
… I hope this openclaw is not connected to the project in any way: https://
x.com/ishaan_jaff/st
atus/2017811361343148167
…
SECURITY
-
LiteLLM Exposes Claude Settings File in Public GitHub Repo
By
–
-
PyPI Security Incident: 425K Downloads Exposure Timeline
By
–
In particular this clarifies the timeline more: 1.82.7 was published 10:39 UTC, PyPI quarantine approx 13:38, so this was up ~3 hours. At 3.4M downloads/day this might be approx ~425K downloads, a lot of that could be non-latest/locked versions so maybe 20K – 80K range exposure.
-
Package Registry Security Economics and Malware Prevention Challenges
By
–
And they mostly shouldn't, can you imagine how uneconomical it would be for a package registry to make guarantees that the packages in that registry are free from malware?
-
Supply Chain Attacks Threaten AI Development Pipelines
By
–
Supply chain attacks on AI tooling is a bit alarming TBH. Most companies just pip install and deploy without auditing dependencies… scary failure mode.
-
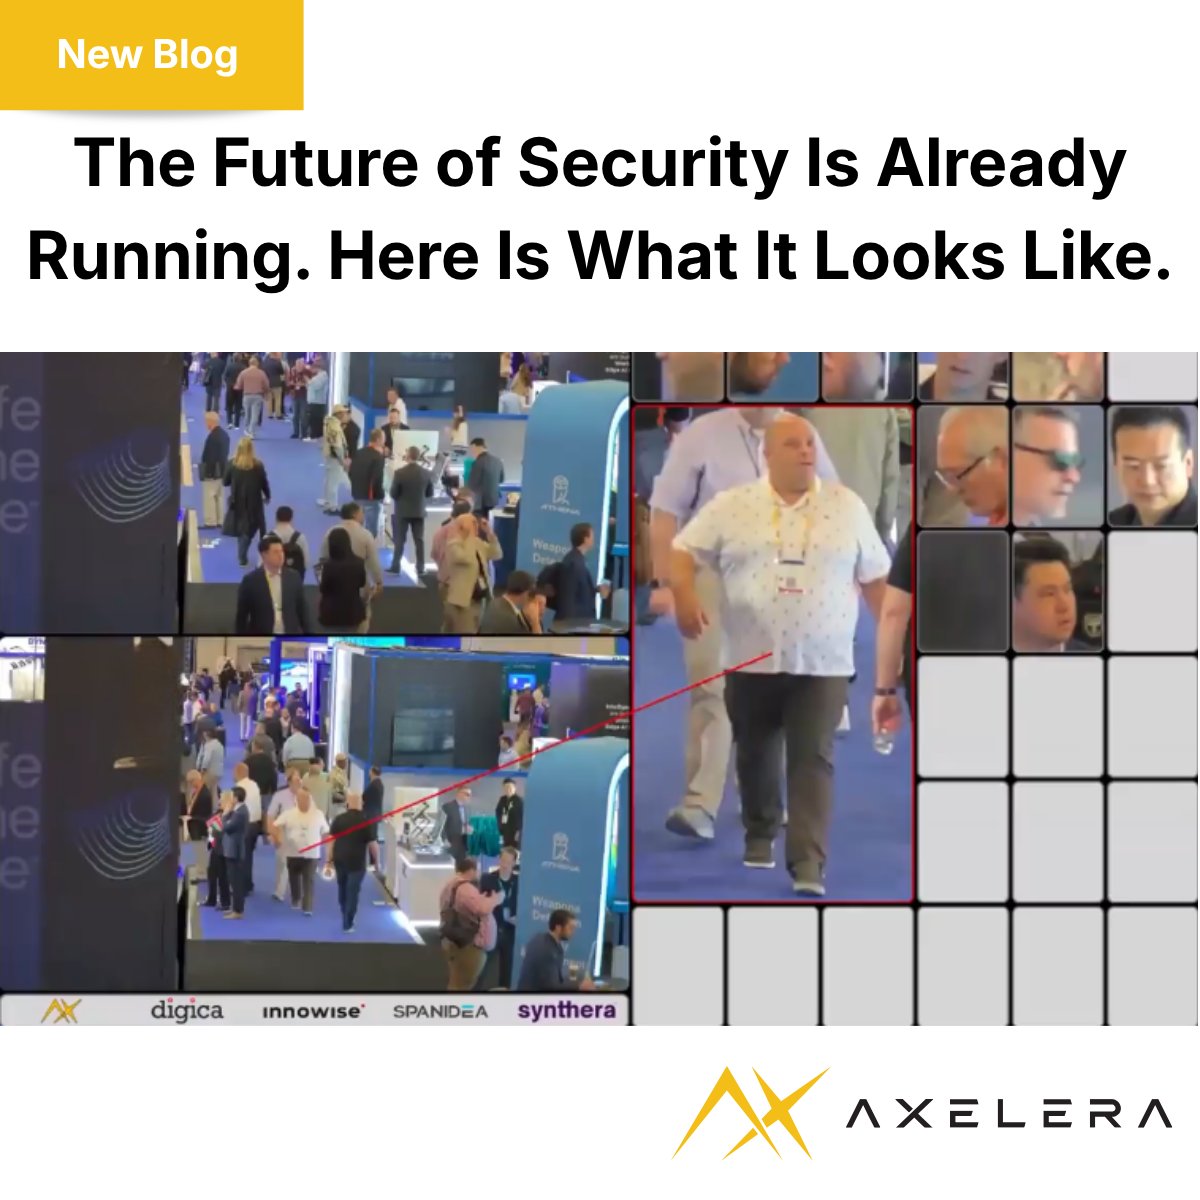
Axelera AI showcases edge AI security at ISC West 2026
By
–
ISC West 2026 opens tomorrow. Find us at Booth 31087 to see live edge AI security in action: 8K cameras, real-time person-of-interest tracking, and novel threat detection, all on a single workstation PC. We also published the business case behind it. eu1.hubs.ly/H0sXbPq0 #ISCWest2026 #EdgeAI #PhysicalSecurity #AxeleraAI
→ View original post on X — @axeleraai, 2026-03-24 20:00 UTC
-
Securing Python Packages: Auditing Source Code to Prevent Supply Chain Attacks
By
–
I think the same thing happened with the ctx package a few years back (also through PyPI). Not perfect, but I think the best way to avoid is to: 1. Download a source code snapshot of the package (e.g., from github) 2. Audit it (traditionally manually, but now also LLM
-

Databricks Launches Lakewatch Cybersecurity Platform Against AI Agents
By
–
Databricks CEO @alighodsi joined @CNBC
's @dee_bosa live from #RSAC2026 to talk about the company's entry into cybersecurity with Lakewatch, and what he sees as a fundamental shift in how organizations defend themselves. Attackers are using AI agents to exploit vulnerabilities in -
PyPI Uses AI Scanning to Detect Malicious Package Attacks
By
–
"just seems like a total no-brainer that PyPi/npm/crates.io/etc. should do AI-powered scans for this pattern of attack" PyPI does that via an API used by scanning partners. I expect that may be why the package was quarantined on PyPI within an hour of it going live
-
Safe Permission Skipping in Claude CLI Interface
By
–
tired: claude –dangerously-skip-permissions
— Bilawal Sidhu (@bilawalsidhu) 24 mars 2026
wired: claude –safely-skip-permissions https://t.co/FxBmnFKUnGtired: claude –dangerously-skip-permissions wired: claude –safely-skip-permissions
-
AI Security Risk: Curated AI Systems Vulnerable to Hacking
By
–
That's one of my great fear. Having curated AI, and connect to other tools with a hack.