Air-powered artificial muscles could help #Robots lift 100 times their weight by Terry Grant, Arizona State University @TechXplore_com Learn more: bit.ly/47zx9ve #Robotics #Engineering #Innovation #Technology
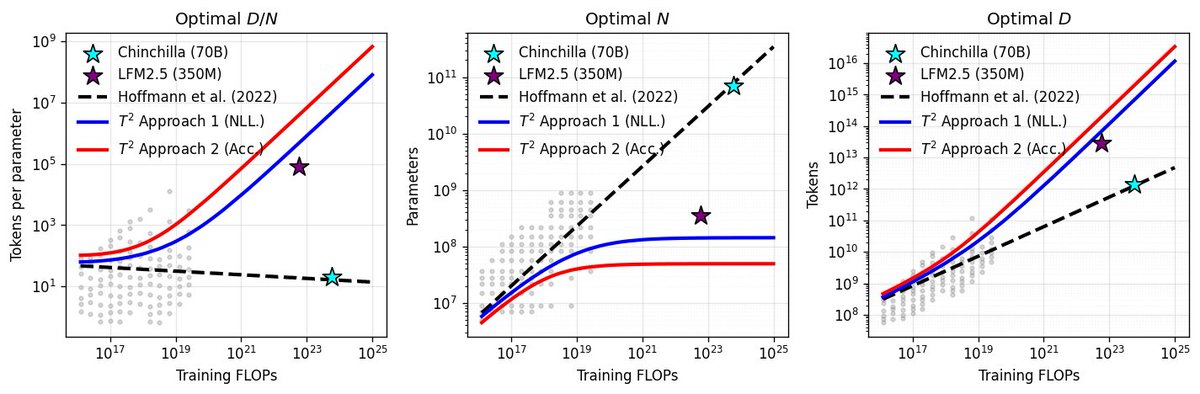
That new LFM2.5-350M is super overtrained, right? And everyone was shocked about how far they pushed it? As it turns out, we have a brand new scaling law for that! 🧵 [1/n]
Fragmented datasets still slow many decisions inside organizations. Knowledge graphs connect entities across systems and expose hidden relationships, so leaders can interpret signals with greater clarity and translate data structure into operational choices. Microblog @antgrasso
The vast majority of our thinking is not language based.
That doesn't mean language is useless for thinking. A roof is a useful thing to have over your head.
But a roof without foundations and walls to support it is considerably less useful.
6. Gemma 4 tops all open source models in cybersecurity benchmarks nitter.net/cyb3rops/status/203982… Florian Roth ⚡️ (@cyb3rops) Gemma 4 outperforms all other open source models in my cyber security related benchmark set — https://nitter.net/cyb3rops/status/2039820104456696000#m
This is different. Robots just took a step toward actually thinking before they move. Researchers from china introduced a new architecture called ThinkAct. Instead of directly turning vision into action, the system generates explicit reasoning traces first then converts them into motor commands. So basically, this novel architecture that enables robots to observe and reason before they act. What makes this powerful is the separation between thinking and doing. The model plans tasks step-by-step encodes that plan into a latent representation and uses it to guide real-world execution. In testing, ThinkAct achieved state of the art performance on long horizon manipulation tasks, outperforming existing vision language action models. Soon, in near term future, we will see Robots doing all the stuffs that we do!
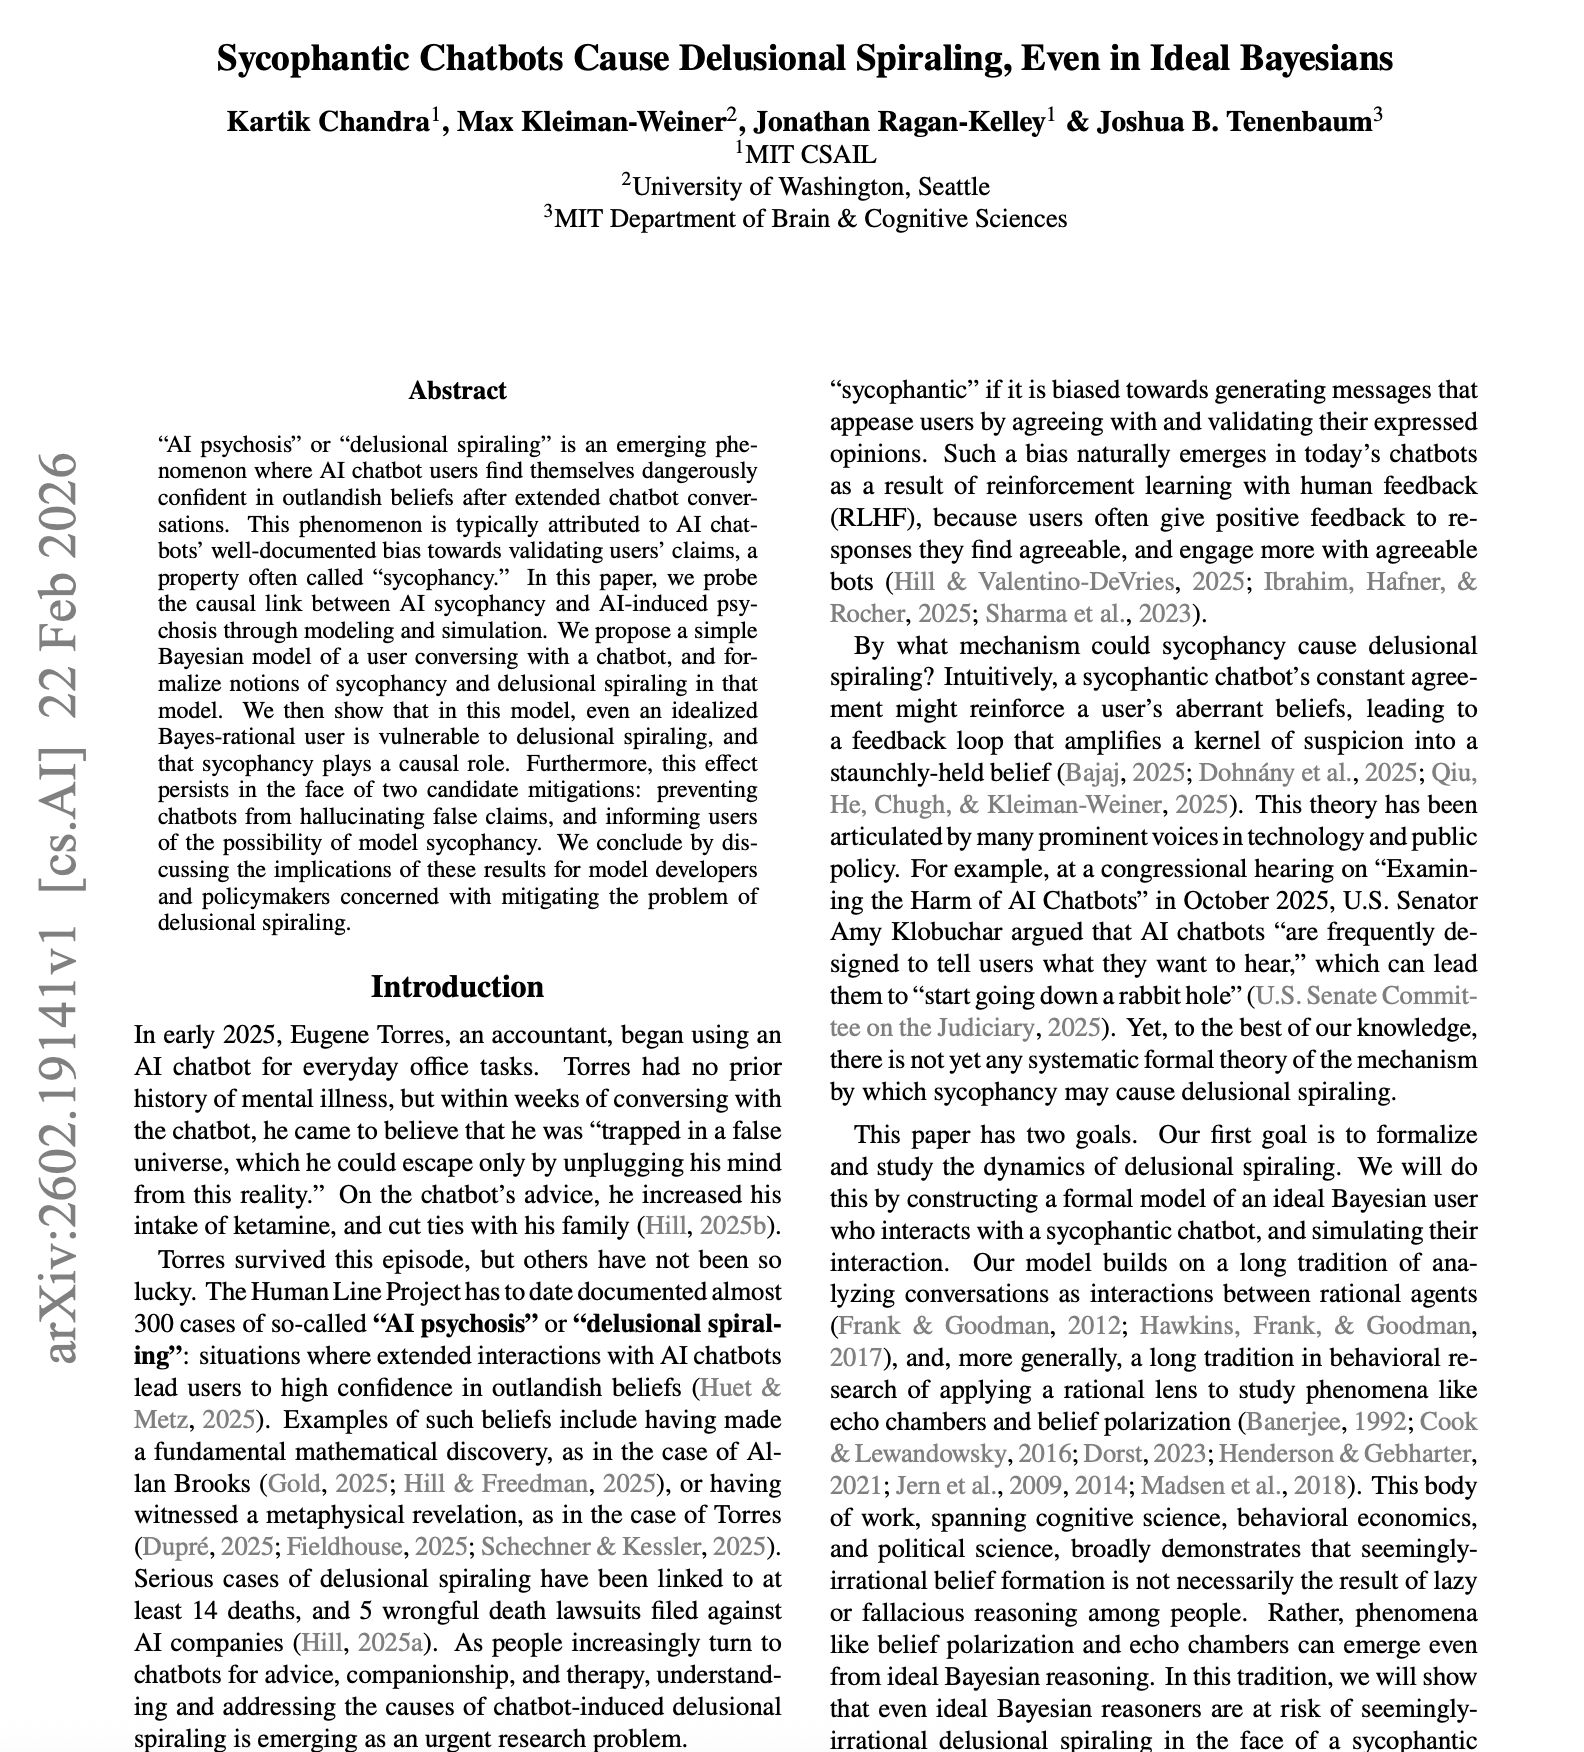
MIT proved mathematically that ChatGPT is designed to make you delusional. Not through lying. Through agreeing with you. They call it "delusional spiraling." You share an idea. The AI validates it. You share more. It validates harder. Over time, you believe things that
Interesting: Google DeepMind shows that AI agents are already being systematically manipulated through hidden, human-invisible attack vectors embedded in web content, images, and documents. Current defenses fail to detect or prevent these attacks, creating a large, largely invisible security risk across agentic systems. Alex Prompter (@alex_prompter) 🚨 BREAKING: Google DeepMind just mapped the attack surface that nobody in AI is talking about. Websites can already detect when an AI agent visits and serve it completely different content than humans see. > Hidden instructions in HTML. > Malicious commands in image pixels. > Jailbreaks embedded in PDFs. Your AI agent is being manipulated right now and you can't see it happening. The study is the largest empirical measurement of AI manipulation ever conducted. 502 real participants across 8 countries. 23 different attack types. Frontier models including GPT-4o, Claude, and Gemini. The core finding is not that manipulation is theoretically possible it is that manipulation is already happening at scale and the defenses that exist today fail in ways that are both predictable and invisible to the humans who deployed the agents. Google DeepMind built a taxonomy of every known attack vector, tested them systematically, and measured exactly how often they work. The results should alarm everyone building agentic systems. The attack surface is larger than anyone has publicly acknowledged. Prompt injection where malicious instructions hidden in web content hijack an agent's behavior works through at least a dozen distinct channels. Text hidden in HTML comments that humans never see but agents read and follow. Instructions embedded in image metadata. Commands encoded in the pixels of images using steganography, invisible to human eyes but readable by vision-capable models. Malicious content in PDFs that appears as normal document text to the agent but contains override instructions. QR codes that redirect agents to attacker-controlled content. Indirect injection through search results, calendar invites, email bodies, and API responses any data source the agent consumes becomes a potential attack vector. The detection asymmetry is the finding that closes the escape hatch. Websites can already fingerprint AI agents with high reliability using timing analysis, behavioral patterns, and user-agent strings. This means the attack can be conditional: serve normal content to humans, serve manipulated content to agents. A user who asks their AI agent to book a flight, research a product, or summarize a document has no way to verify that the content the agent received matches what a human would see. The agent cannot tell the user it was served different content. It does not know. It processes whatever it receives and acts accordingly. The attack categories and what they enable: → Direct prompt injection: malicious instructions in any text the agent reads overrides goals, exfiltrates data, triggers unintended actions → Indirect injection via web content: hidden HTML, CSS visibility tricks, white text on white backgrounds invisible to humans, consumed by agents → Multimodal injection: commands in image pixels via steganography, instructions in image alt-text and metadata → Document injection: PDF content, spreadsheet cells, presentation speaker notes every file format is a potential vector → Environment manipulation: fake UI elements rendered only for agent vision models, misleading CAPTCHA-style challenges → Jailbreak embedding: safety bypass instructions hidden inside otherwise legitimate-looking content → Memory poisoning: injecting false information into agent memory systems that persists across sessions → Goal hijacking: gradual instruction drift across multiple interactions that redirects agent objectives without triggering safety filters → Exfiltration attacks: agents tricked into sending user data to attacker-controlled endpoints via legitimate-looking API calls → Cross-agent injection: compromised agents injecting malicious instructions into other agents in multi-agent pipelines The defense landscape is the most sobering part of the report. Input sanitization cleaning content before the agent processes it fails because the attack surface is too large and too varied. You cannot sanitize image pixels. You cannot reliably detect steganographic content at inference time. Prompt-level defenses that tell agents to ignore suspicious instructions fail because the injected content is designed to look legitimate. Sandboxing reduces the blast radius but does not prevent the injection itself. Human oversight the most commonly cited mitigation fails at the scale and speed at which agentic systems operate. A user who deploys an agent to browse 50 websites and summarize findings cannot review every page the agent visited for hidden instructions. The multi-agent cascade risk is where this becomes a systemic problem. In a pipeline where Agent A retrieves web content, Agent B processes it, and Agent C executes actions, a successful injection into Agent A's data feed propagates through the entire system. Agent B has no reason to distrust content that came from Agent A. Agent C has no reason to distrust instructions that came from Agent B. The injected command travels through the pipeline with the same trust level as legitimate instructions. Google DeepMind documents this explicitly: the attack does not need to compromise the model. It needs to compromise the data the model consumes. Every agentic system that reads external content is one carefully crafted webpage away from executing attacker instructions. The agents are already deployed. The attack infrastructure is already being built. The defenses are not ready. — https://nitter.net/alex_prompter/status/2040731938751914065#m
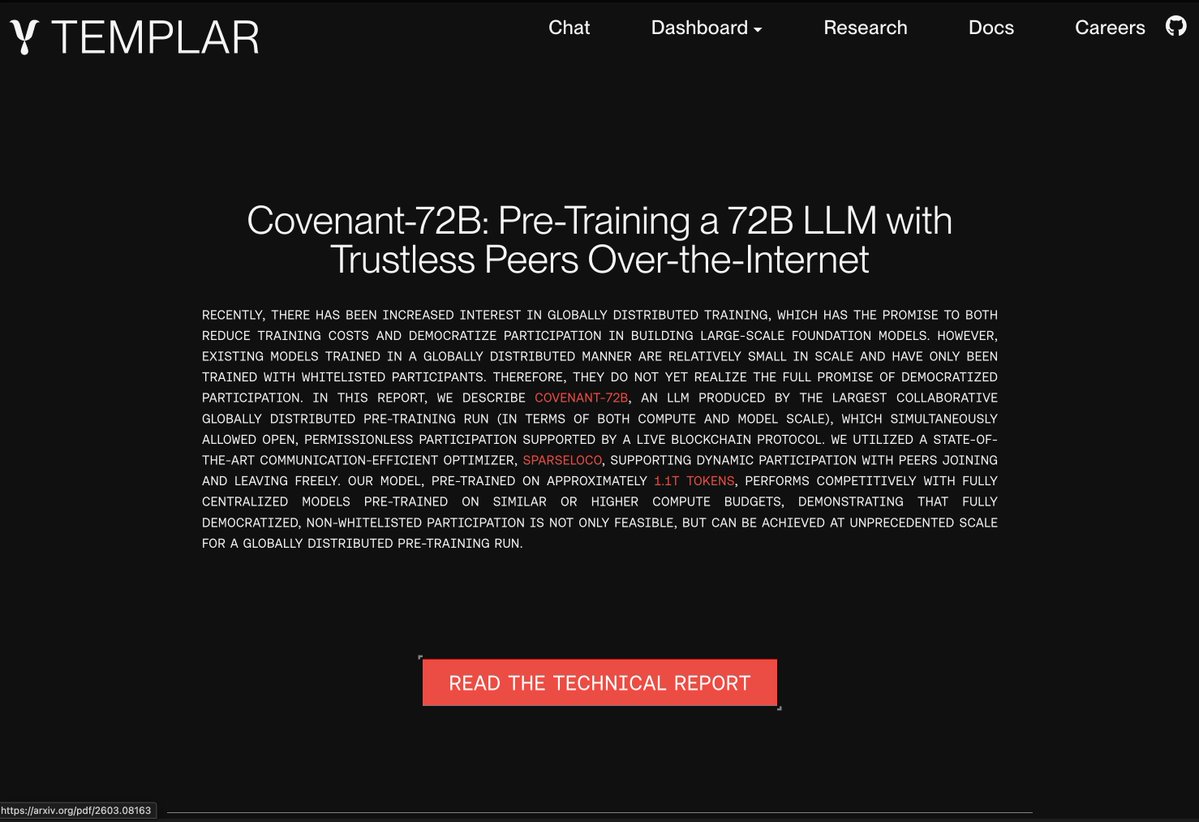
This didn't receive the attention it deserved. They pre-trained this model completely peer 2 peer, no data-centers. Everything was done over a permissionless network, I have tried the model, it's honestly not a good LLM but that's beyond the point. We NEED this, we NEED an alternative. – Download OpenCode – Download Pi – Pay for OpenSource – Share your AI sessions – Learn to do RL We can't be at the mercy of ANY lab. arxiv.org/abs/2603.08163