We’ve been using harness in sandboxes + MCP gateway to have tight controls on the data flow. It works really well.
SECURITY
-
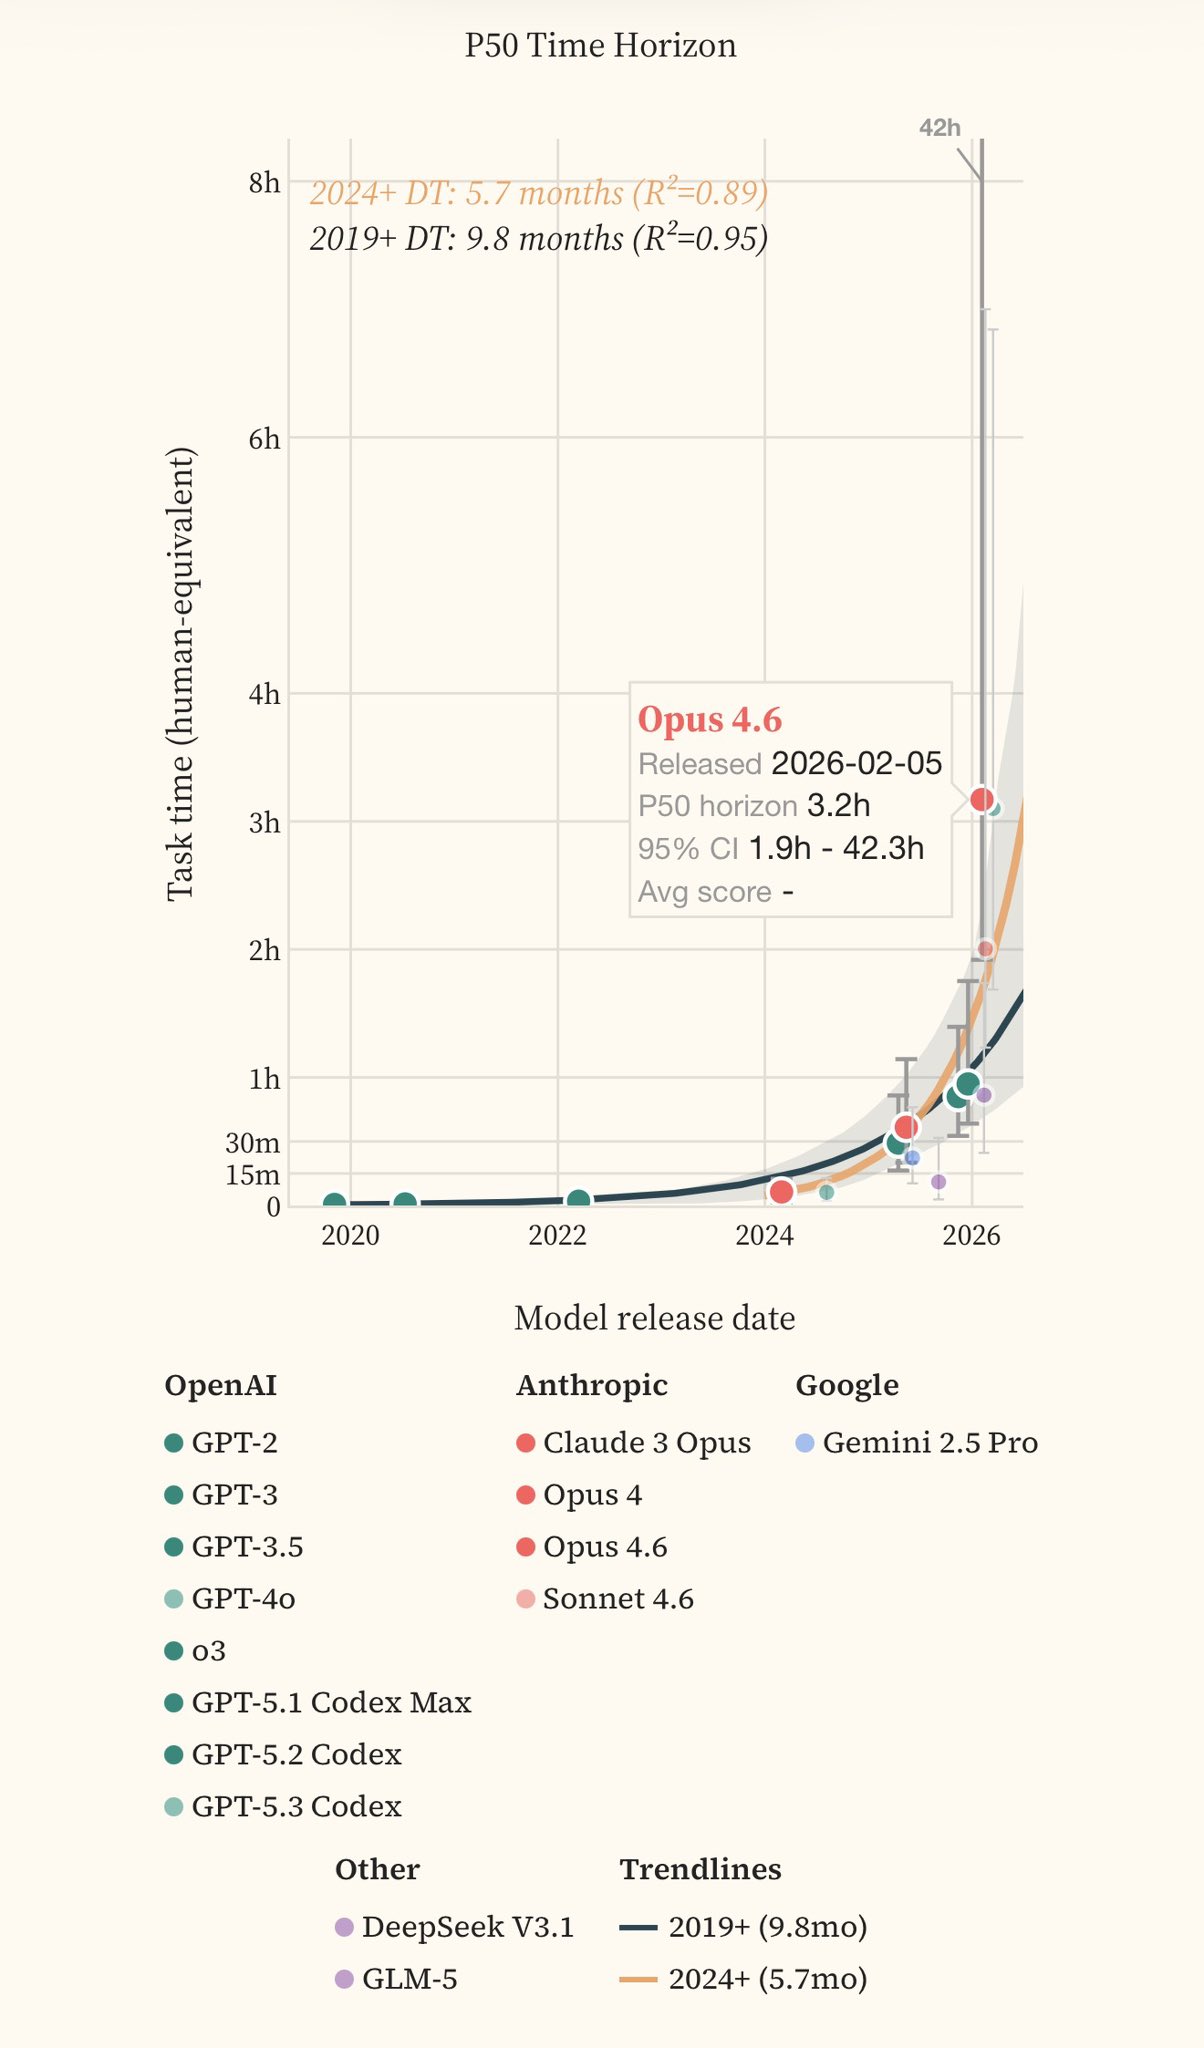
Impact of token limits on AI agent performance in cybersecurity
By
–
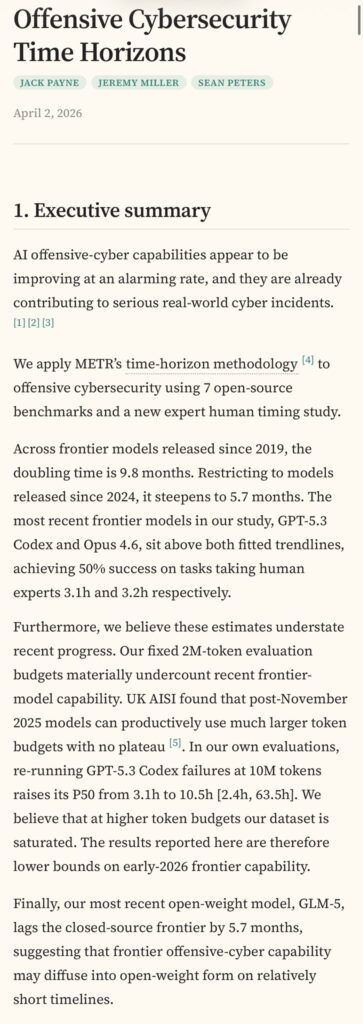
Real world example: raising token limits from 3M to 10M tripled the amount of work that Codex could do independently on cybersecurity tasks. From 3.1 hours to 10.5 hours.
-
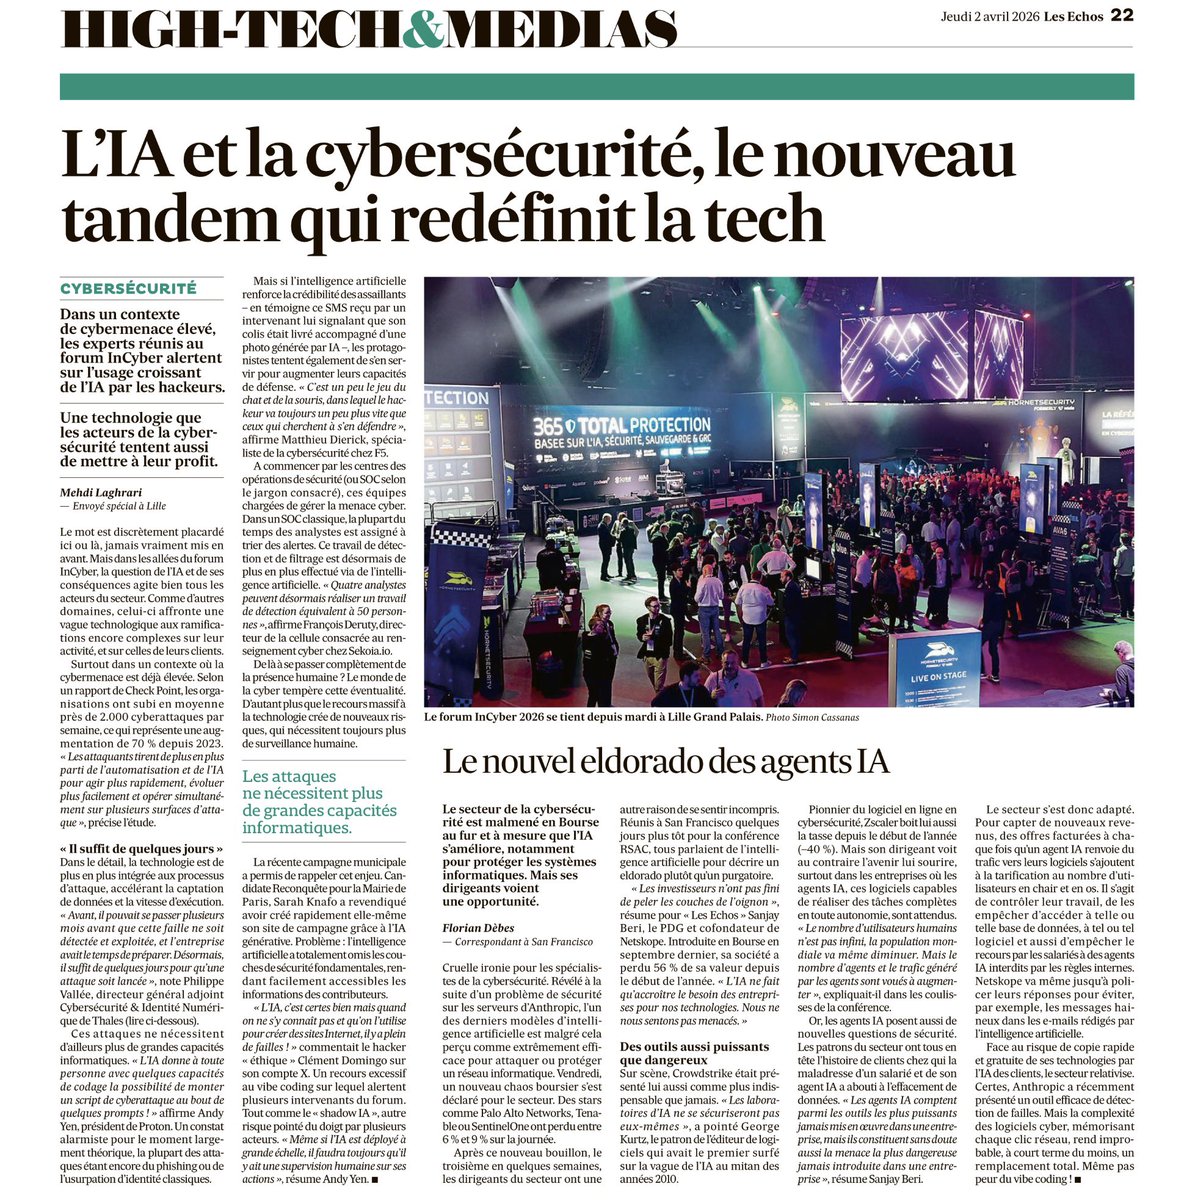
AI Has Democratized Computer Hacking
By
–
Before, a cyberattack required months of preparation and rare skills. Today, anyone can code an attack script in just a few prompts. Result: +70% cyberattacks since 2023. AI didn't just arm hackers. It democratized hacking. [Translated from EN to English]
→ View original post on X — @alex_tsico, 2026-04-05 18:08 UTC
-
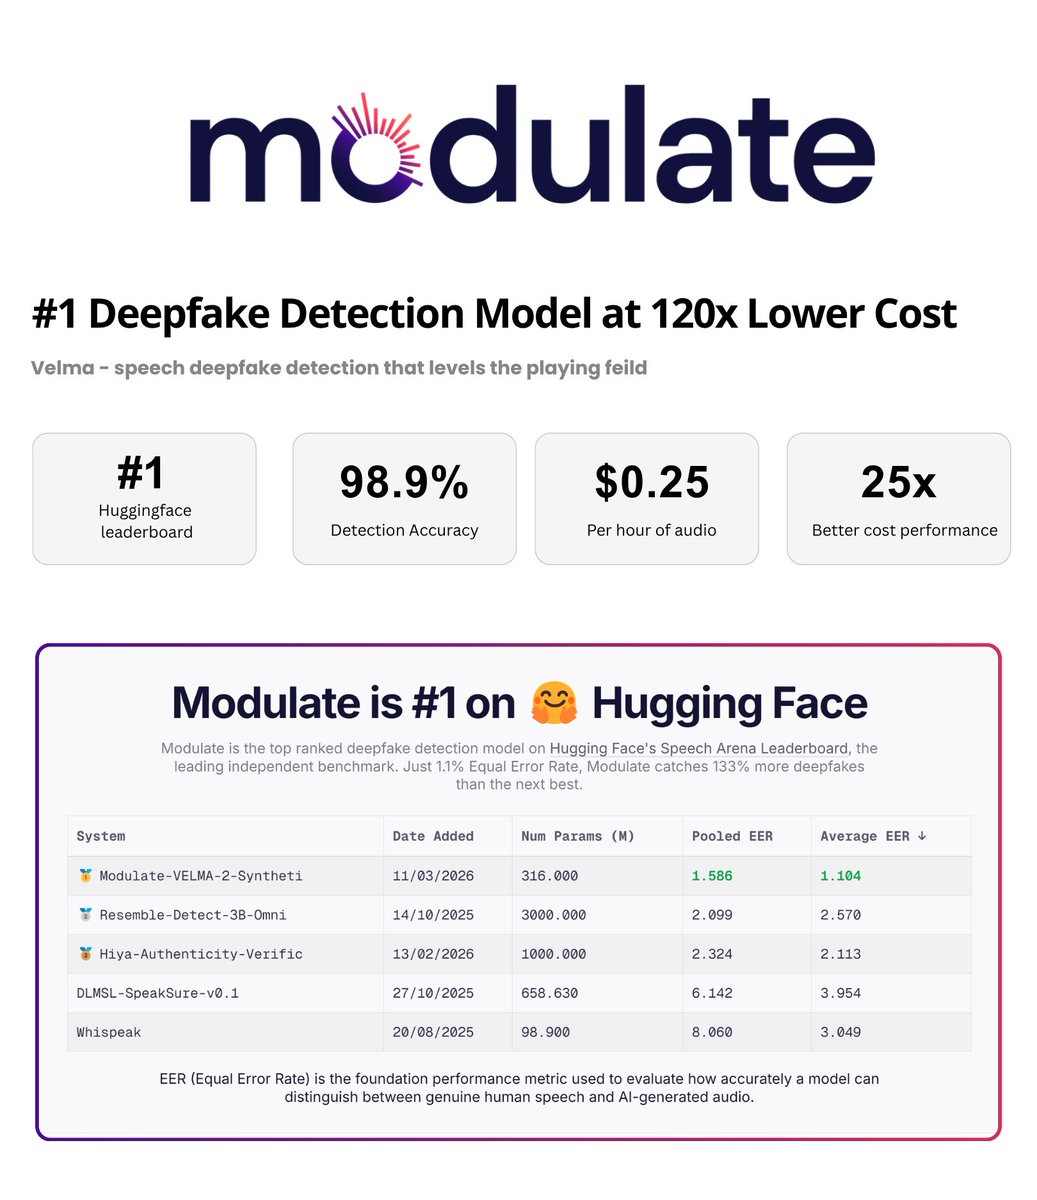
Modulate’s Velma: Real-Time Deepfake Voice Detection API
By
–
If you found it useful, reshare it with your network Follow me → @Sumanth_077 for more insights and tutorials on AI Engineering! nitter.net/Sumanth_077/status/204… Sumanth (@Sumanth_077) Massive breakthrough in voice deepfake detection! @modulate_ai just released a deepfake detection API that topped @huggingface's leaderboard at 98.9% accuracy. Here's the problem with how most companies handle deepfake detection. They check the first 10 seconds of a call. If it passes, they assume the whole call is clean. Gate check. One scan. Done. Fraudsters know this. So they open the call with a real voice. Their own voice, a colleague, a quick recording. Pass the check. Then switch to the AI-generated clone mid-call. The system already gave them the green light. They're through. The fix is obvious. Monitor the entire call. Not just the opening. Not random spot checks. Every segment, continuously, in real-time. But that was too expensive. Until now. Velma is Modulate's real-time and batch deepfake detection API. Here's what changed. • Real-time streaming detection. Analyzes audio every 2 seconds during live calls. Catches mid-call voice switches instantly. • 120x cheaper than competitors. $0.25 per hour instead of $30-150. Now you can actually afford to monitor full conversations instead of spot-checking. • Only needs 2.5 seconds of audio. Faster detection, works with short segments. • 98.9% accuracy, ranked first on HuggingFace. Lower error rate than models 10x larger. First 1000 API credits are free. I've shared the link in the replies! — https://nitter.net/Sumanth_077/status/2040793953927311527#m
→ View original post on X — @sumanth_077, 2026-04-05 14:12 UTC
-

Checkout Modulate Deepfake Detection API
By
–
Checkout Modulate: modulate.ai/api/deepfake-det…
→ View original post on X — @sumanth_077, 2026-04-05 14:09 UTC
-

Modulate’s Velma API Achieves 98.9% Deepfake Detection Accuracy
By
–
Massive breakthrough in voice deepfake detection! @modulate_ai just released a deepfake detection API that topped @huggingface's leaderboard at 98.9% accuracy. Here's the problem with how most companies handle deepfake detection. They check the first 10 seconds of a call. If it passes, they assume the whole call is clean. Gate check. One scan. Done. Fraudsters know this. So they open the call with a real voice. Their own voice, a colleague, a quick recording. Pass the check. Then switch to the AI-generated clone mid-call. The system already gave them the green light. They're through. The fix is obvious. Monitor the entire call. Not just the opening. Not random spot checks. Every segment, continuously, in real-time. But that was too expensive. Until now. Velma is Modulate's real-time and batch deepfake detection API. Here's what changed. • Real-time streaming detection. Analyzes audio every 2 seconds during live calls. Catches mid-call voice switches instantly. • 120x cheaper than competitors. $0.25 per hour instead of $30-150. Now you can actually afford to monitor full conversations instead of spot-checking. • Only needs 2.5 seconds of audio. Faster detection, works with short segments. • 98.9% accuracy, ranked first on HuggingFace. Lower error rate than models 10x larger. First 1000 API credits are free. I've shared the link in the replies!
→ View original post on X — @sumanth_077, 2026-04-05 14:09 UTC
-
Intelligence Services Can Easily Penetrate Technology Secrecy Systems
By
–
I expect the secrecy around them is easily penetrated by any remotely competent intelligence service – thousands of people must be in the loop, and they will have signed NDAs, not military-grade secrets laws
-
Legacy Context Risks in AI Agent Development and Coding
By
–
you can't. legacy makes no sense for coding or agentic work. far too risky re prompt injection too.
-
Ukraine Leverages AI-Guided Warfare for Asymmetric Advantage
By
–
Ukraine showing how AI-guided war leads to asymmetric advantage. This has a lot to do with @PalantirTech’s Project Maven. https://t.co/3ucylnyaqH
— Nina Schick (@NinaDSchick) 4 avril 2026Ukraine showing how AI-guided war leads to asymmetric advantage. This has a lot to do with @PalantirTech
’s Project Maven. -
CISOs Prioritize OT/IT Convergence for Enhanced Security
By
–
More CISOs are looking at OT/IT convergence seriously. CC: @IIoT_World @CRudinschi @agentic_factory @survivingwithan @joannefriedman @bzarkout