This is a good use case for AI. Better than letting suspects flee.
SECURITY
-
OpenClaw Repository Takes Step Against Spam
By
–
This is very welcome and a small but meaningful step to fight spam on the openclaw repo.
-

AI Data Security: Organizations Face Sensitive Data Exposure Risks
By
–
𝗦𝗰𝗮𝗿𝘆 𝘀𝘁𝗮𝘁𝘀: 90% of organizations have sensitive data surfaceable by AI. 46% of all breaches involve customer PII. 40% involve employee PII. 𝗛𝗲𝗹𝗽 𝗶𝘀 𝗵𝗲𝗿𝗲: @Commvault Extends Enterprise Resilience to Structured & AI Data with Real-Time Governance Controls.
-
Disproportionate blocking prevents work productivity
By
–
Bon c'était pas un gros harcèlement mais le résultat c'est un blocage disproportionné qui empêche de bosser.
-

Disable microphone surveillance on AI tools and services
By
–
It’s always listening How else would we improve Gemini?? It’s for the good of humanity, let it spy on you. Just kidding! Make sure you disable continuous microphone usage on most tools and check for settings on how they leverage your data! A lot of company have a “use
-
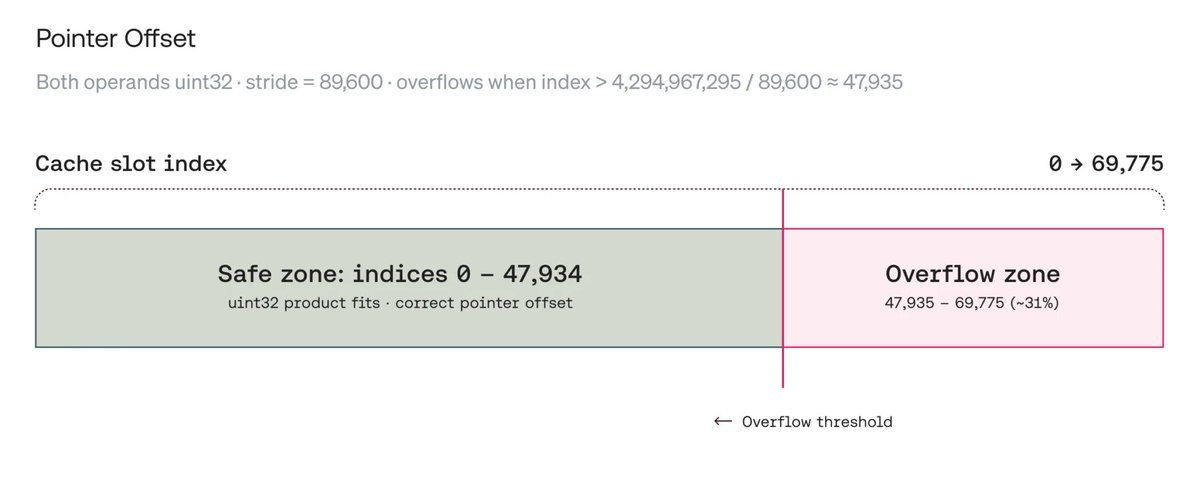
Silent 32-bit Integer Overflow in vLLM Mamba-1 CUDA Kernel
By
–
3/4 Root cause: a silent 32-bit integer overflow inside a vLLM CUDA kernel for Mamba-1 selective scan forward kernel. cache_index * ssm_states_batch_stride overflowed once cache slots got large enough, corrupting writes with no crash and no warning.
-
French Army struggles with drone swarm deployment capability
By
–
Comment allons-nous faire pour contrer ça? En France, l'Armée de Terre a du mal à envoyer 3 drones DJI en essaim… https://t.co/ZDuM8EX8JH
— Olivier Rimmel 🕊️ (@OlivierRimmel) 26 mars 2026Comment allons-nous faire pour contrer ça? En France, l'Armée de Terre a du mal à envoyer 3 drones DJI en essaim…
-

MCP Security: Avoid Local Servers, Run Remote Containers
By
–
PSA: Stop running local MCP servers. The folks at futuresearch were pwned when a local MCP server pulled in an impacted package. Always run your MCP servers remotely. The blast radius should be limited to the container that it runs in. If you're impacted by the LiteLLM
-

MCP Server Security: Avoid Local Deployment After LiteLLM Breach
By
–
PSA: Stop running local MCP servers. The folks at futuresearch were pwned when a local MCP server pulled in an impacted package. Always run your MCP servers remotely. The blast radius should be limited to the container that it runs in. If you're impacted by the LiteLLM
-

MCP Server Security: Avoid Local Deployment Risks
By
–
PSA: Stop running local MCP servers. The folks at futuresearch were pwned when a local MCP server pulled in an impacted package. Always run your MCP servers remotely. The blast radius should be limited to the container that it runs in. If you're impacted by the LiteLLM