Looks confirmed, as @jadennguyen_me already captured a snapshot of Claude Code's source, archived for *security research* → https://
github.com/dam2onkid/clau
de-code
… https://
github.com/dam2onkid/clau
de-code
…
SECURITY
-
Claude Code source code leaked for security research
By
–
-

Claude Code Leak Reveals Capybara Model
By
–


BREAKING : Claude Code source code has been leaked via the map file in Anthropic's npm registry. The code references an unreleased model named "Capybara", mentioned in the recently revealed blog post. UNDERCOVER MODE
-
Anthropic Package Removal: GitHub Archive Remains Permanent
By
–
Anthropic pulled the package and deleted older versions from the registry but the GitHub archive is already permanent. That's how npm incidents work in 2026 and they know it.
-
Voice biometrics security vulnerabilities in device authentication systems
By
–
allez, balançons une brique dans la fenêtre sur un problème securité. Y a t'il des applications ou device qui se debloquent avec l'empreinte vocal ? arnaque au président. Voilà, demerdez vous avec ça
-

Claude Source Code Allegedly Leaked Through npm Map File
By
–
WILD if true. @Fried_rice is reporting that Claude's source code leaked via an npm .map file Code: …
https://pub-ae
a8527898604c1bbb12468b1581d95e.r2.dev/src.zip -
Google Quantum Computing Bitcoin Private Key Recovery
By
–
Google should do the right thing and use their new quantum superpowers to help that guy who lost the private key to his bitcoin wallet with like $100m in it lol
-
Active Supply Chain Attack Targets Axios Platform
By
–
In case you haven’t seen the news about the active supply chain attack targeting Axios:
-
Check Axios Supply-Chain Attack Compromise Free Claude Skill
By
–
🚨 Want to quickly check if you've been compromised by the Axios supply-chain attack?
— Charly Wargnier (@DataChaz) 31 mars 2026
Hari (@hrkrshnn) just shipped a free @claudeai skill for us 🙏
/plugin marketplace add cantinasec/plugins
/plugin install cantinasec@cantinasec-plugins
/reload-plugins
/cantinasec:axios pic.twitter.com/XlUdHdDcl7Want to quickly check if you've been compromised by the Axios supply-chain attack? Hari (
@hrkrshnn
) just shipped a free @claudeai skill for us /plugin marketplace add cantinasec/plugins
/plugin install cantinasec@cantinasec-plugins
/reload-plugins /cantinasec:axios -
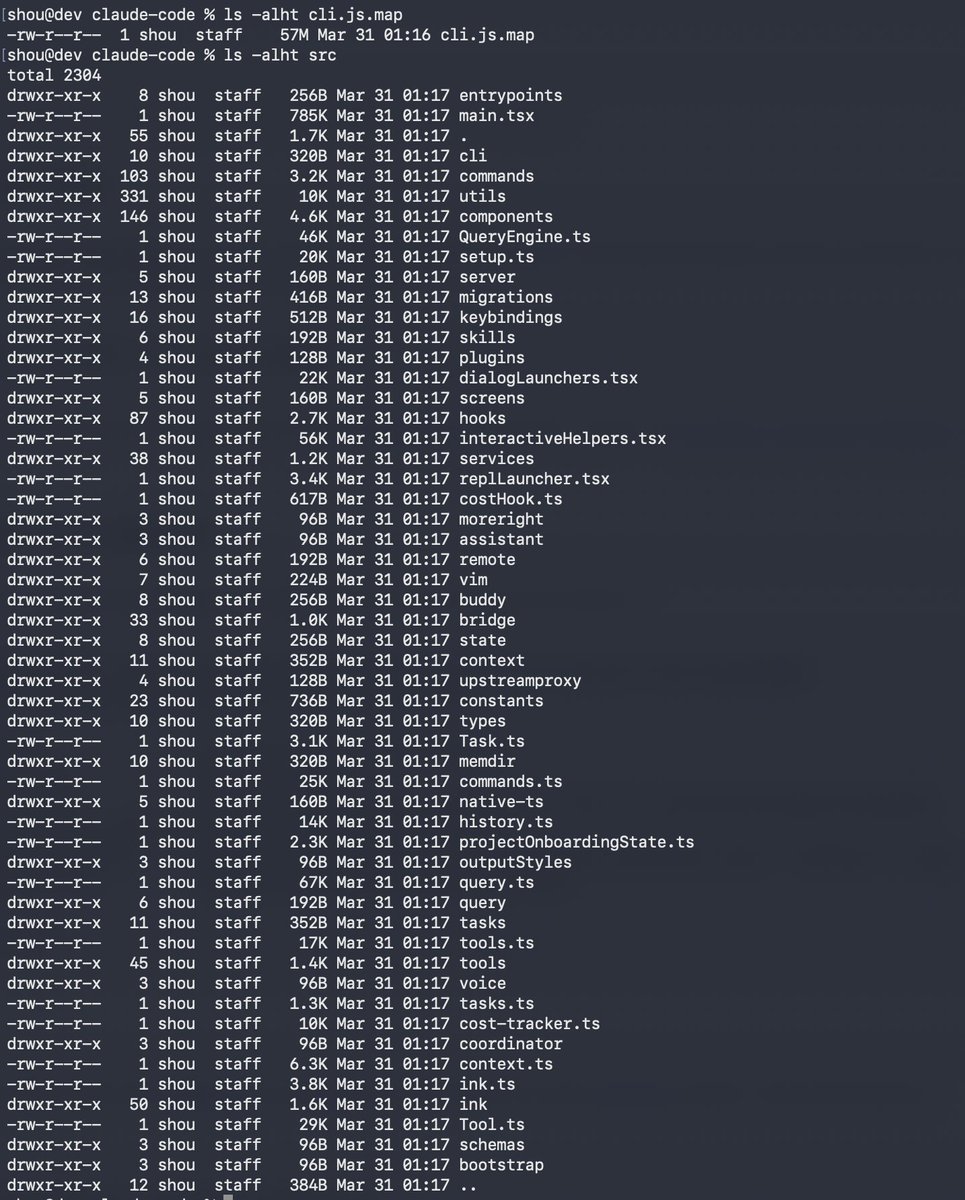
Claude source code allegedly leaked through npm registry map file
By
–
Holy shxt… Chaofan Shou (@Fried_rice) Claude code source code has been leaked via a map file in their npm registry! Code: pub-aea8527898604c1bbb12468b… — https://nitter.net/Fried_rice/status/2038894956459290963#m
→ View original post on X — @arrakis_ai, 2026-03-31 11:15 UTC
-
Open Source Vulnerabilities Threaten AI Application Supply Chain
By
–
The axios attack is a reminder that our entire stack runs on trust in a handful of maintainers. Scary when you think about how many AI apps depend on these packages.