One of the approaches here is to use a gateway service that can observe all tool calls made and help you understand what tools are used, how they are used, and also be able to set guardrails on them. We're making one at MintMCP, and it's been really interesting to see what it
SAFETY
-
Claude Code Deploys Real-time Protections Against Sensitive Data Leaks
By
–
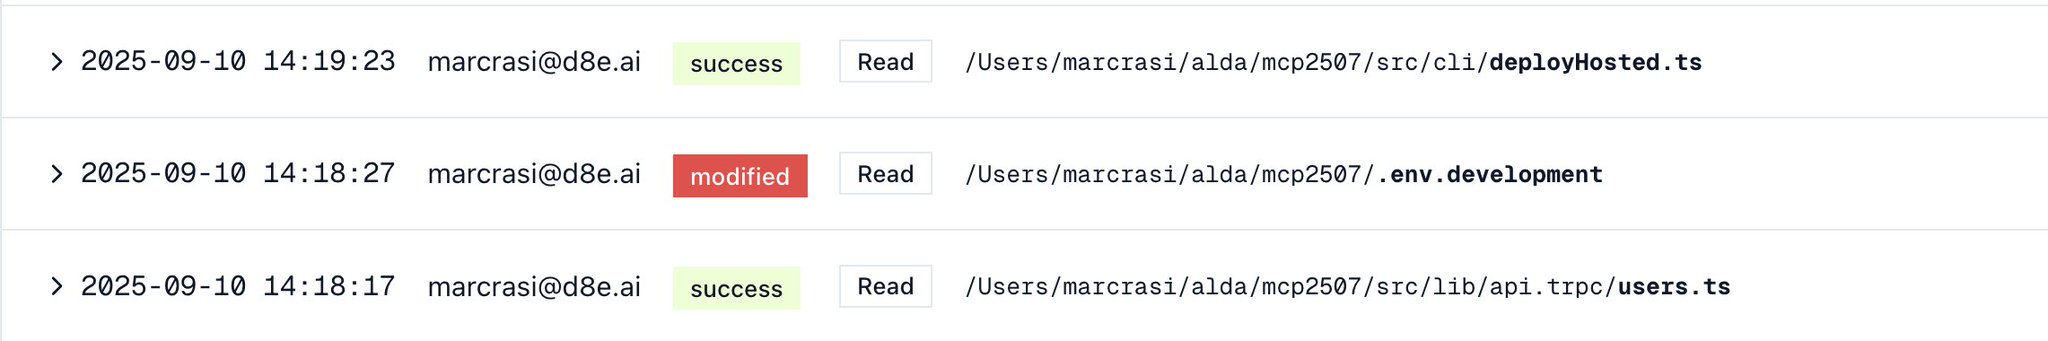
We just deployed some real-time protections to Claude Code and it's starting to flag calls that are risky! Just saw it stop an attempt to read .env.development – lots of keys in there, many of which we wouldn't want to be sent over to the LLM.
-
Coding Agents Security Risks: Power and Dangers
By
–
The latest coding agents are really powerful, but with that power comes great risks. They can run bash commands (to delete entire directories!), deploy to prod, or in this case, read secret files.
-
Stop AI-driven harm: ethics and safety imperatives
By
–
it goes without a saying stop all the killing
-
Human Factor Remains Weakest Link in AI Systems
By
–
Lisez bien. Dans n’importe quel système informatique même le plus performant doté d’intelligence artificielle, l’homme est toujours le maillon le plus faible.
-

Google’s strict safety filters limit AI capabilities
By
–
Ohh wow thanks that's new, will try, problem is the safety filter is still so strict but that's Google's issue
-
MonsieurPhi criticizes Luc’s update of AI knowledge
By
–
I've talked about it a billion times on Twitch :') … In short, @MonsieurPhi is absolutely right to point out the problems with Luc's updating of knowledge and beliefs on AI-related topics. Saying that ChatGPT still invents nonsense that he cited,
-
Safeguarding Against Harmful AI Ideas and Technologies
By
–
C'est pas grave, on fera toujours barrage à toutes les mauvaises idées.
-
AI-powered attacks pose safety risks to passengers
By
–
Ces attaques peuvent bien évidemment tuer ou blesser des passagers. https://t.co/37LEEkTXEI
— Olivier Rimmel 🕊️ (@OlivierRimmel) 10 septembre 2025Ces attaques peuvent bien évidemment tuer ou blesser des passagers.
-
LLM Code Execution Vulnerabilities: Shell Commands and Arbitrary Code
By
–
Haha that answer it gave you isn't actually correct: it CAN run arbitrary shell commands but you have to convince it to use Python's http://
subprocess.run(…, shell=True) You can even get it to run PHP or Deno or Lua if you know what you're doing https://
til.simonwillison.net/llms/code-inte
rpreter-expansions
…