
Most agent queries come from personal use (55%), followed by professional (30%) and educational (16%) contexts. New users often start with low-stakes questions like travel or trivia. Over time, they shift to more complex topics like productivity, learning, and career advice.
@perplexity_ai
-

Agent Activity Dominated by Productivity and Learning Work
By
–
More than half of all agent activity focuses on cognitive work. Agent use is dominated by Productivity & Workflow (36% of queries) and Learning & Research (21%). Users rely on the assistant to think through something, synthesize findings, and take action on those learnings.
-
Harvard Perplexity Study Reveals Large-Scale AI Agent User Behavior
By
–
Harvard and Perplexity researchers conducted the first large‑scale field study of how people use AI agents. We analyzed hundreds of millions of anonymized user interactions in Comet to answer three questions: who’s using agents, how much, and what for.
-
BrowseSafe Open-Source Tool Hardens Autonomous Agents Against Prompt Injection
By
–
BrowseSafe and BrowseSafe-Bench are fully open-source. Any developer building autonomous agents can immediately harden their systems against prompt injection. Read more:
-
BrowseSafe Fine-Tuned Model Outperforms Safety Classifiers
By
–
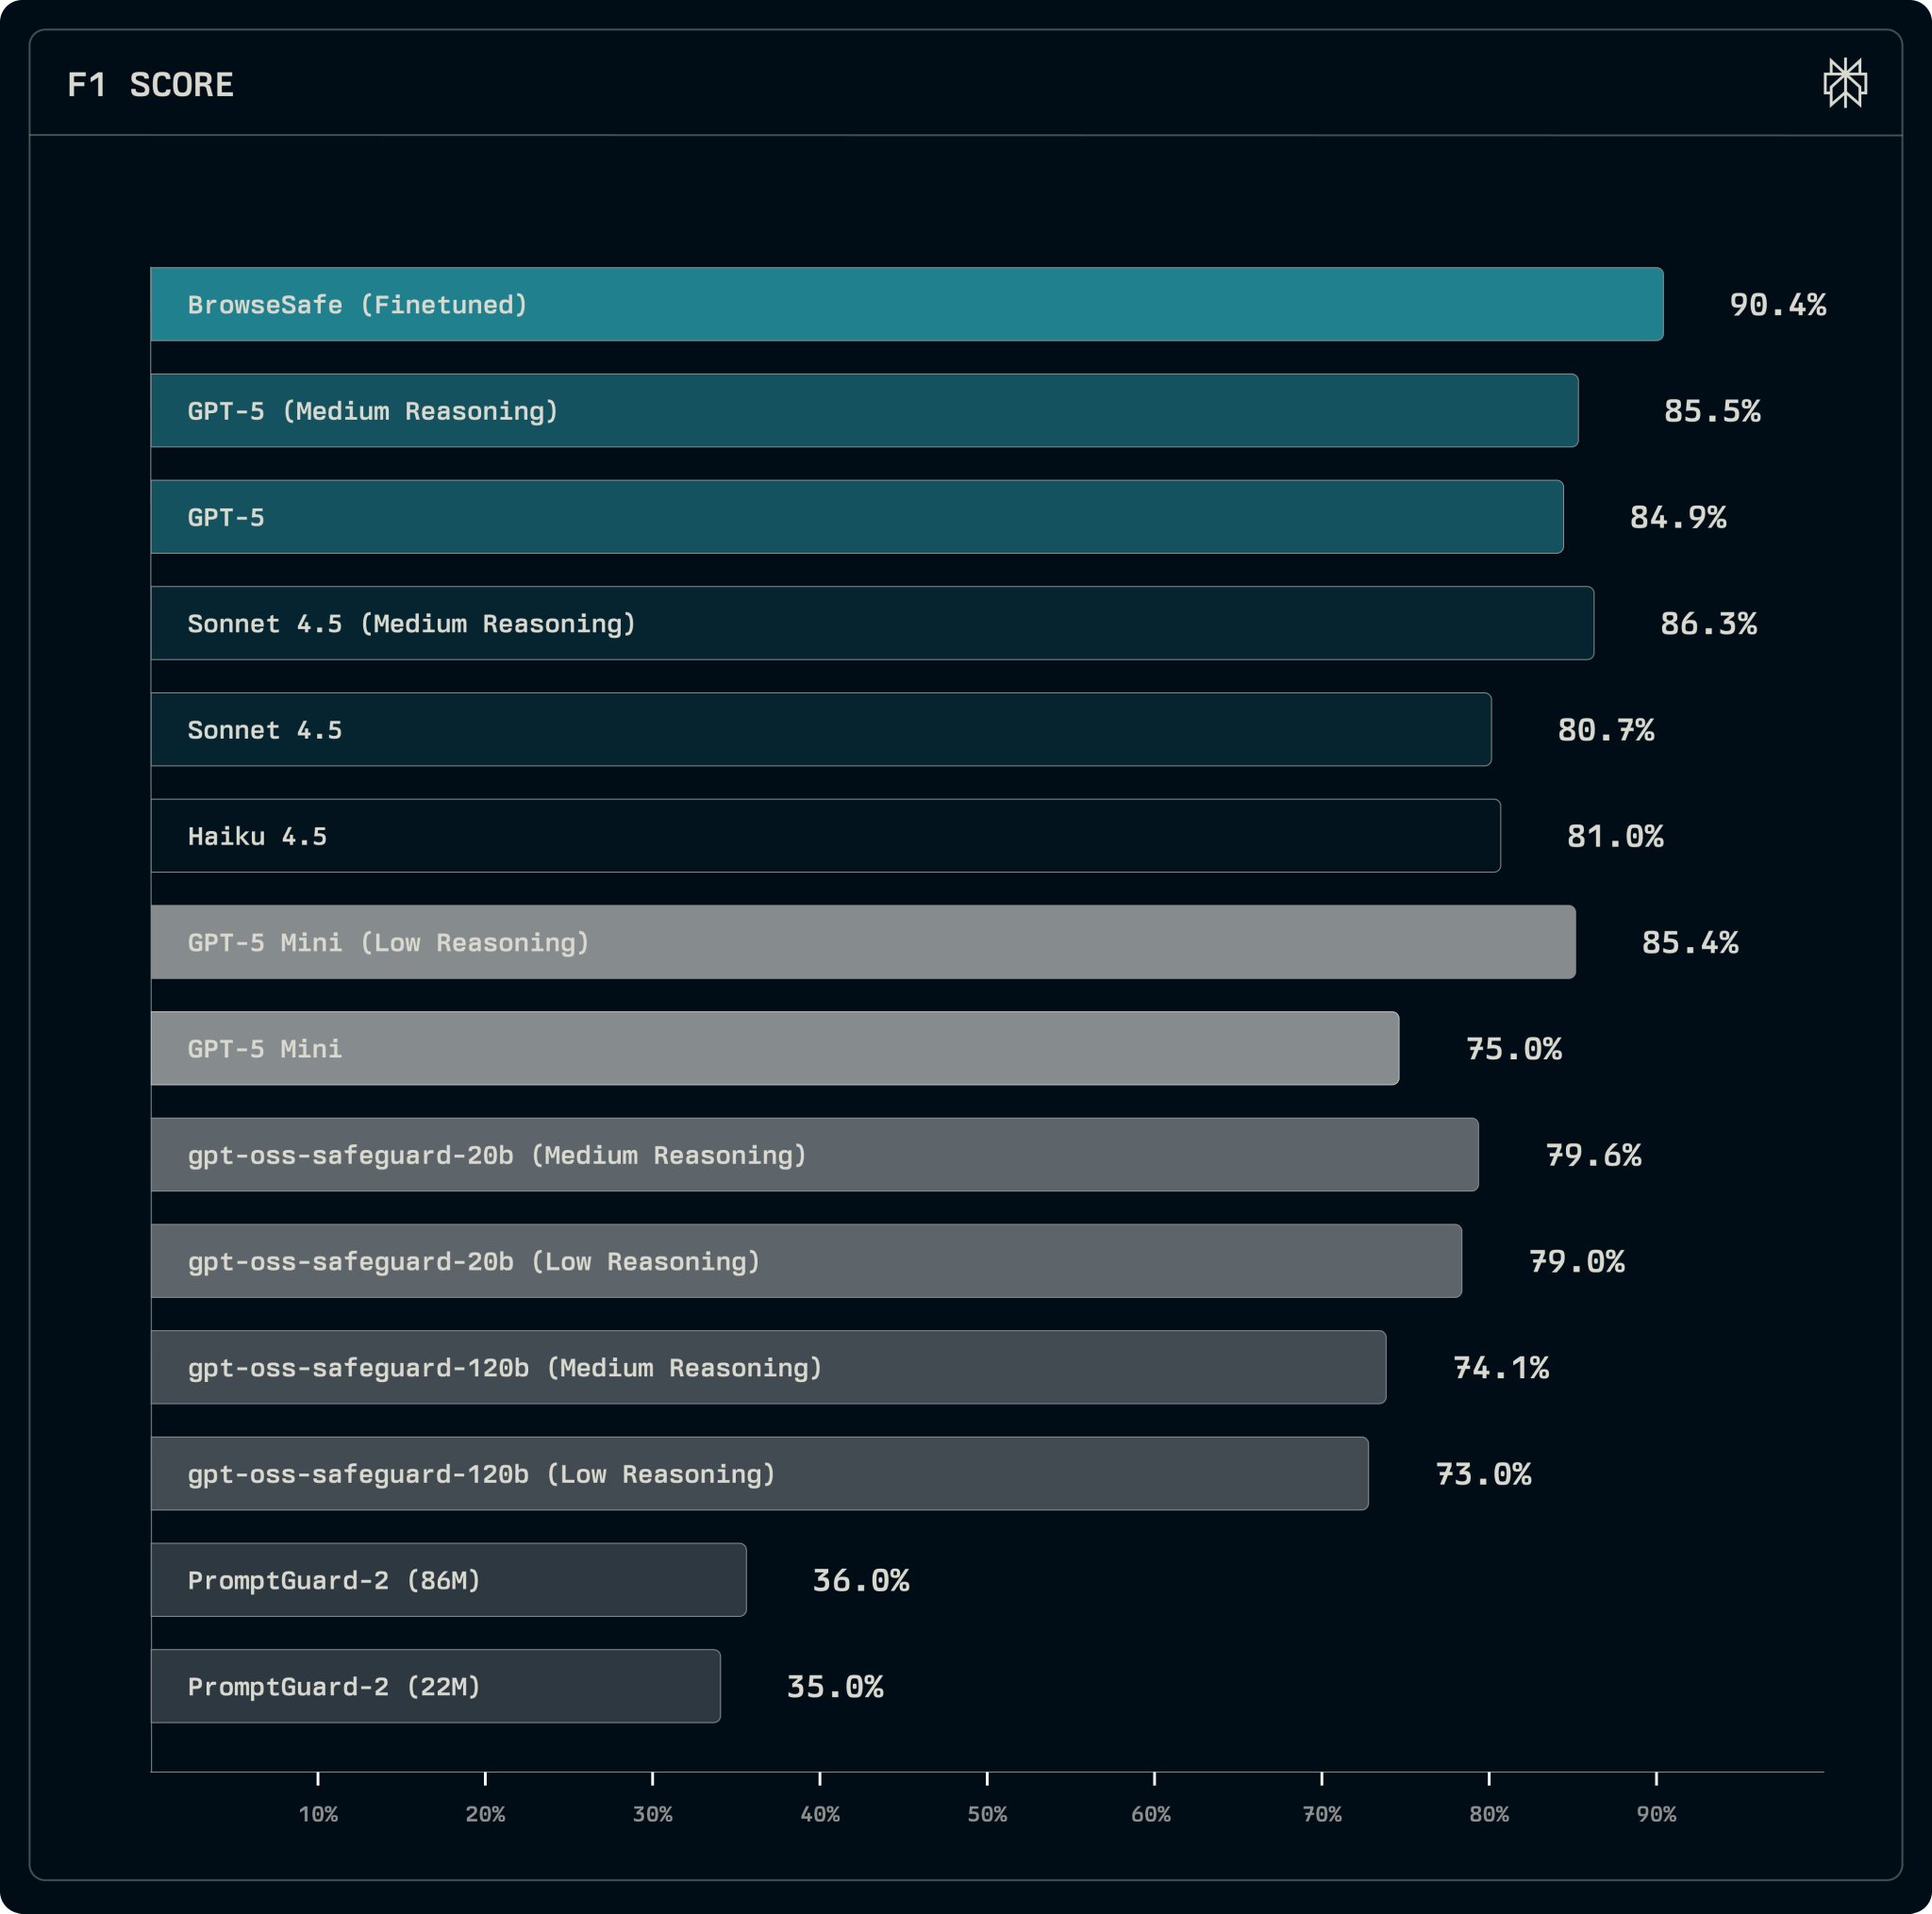
Our findings show that our fine-tuned BrowseSafe model outperforms both off‑the‑shelf safety classifiers and frontier LLMs used as detectors. These gains are possible through fine-tuning on BrowseSafe-Bench data, allowing us to bypass the reasoning latency of larger models.
-
BrowseSafe: Detection Model Against Prompt Injection Attacks
By
–
BrowseSafe is a specialized detection model to defend against evolving prompt injection attacks. It is designed specifically to spot and block malicious instructions hidden in web pages before they can impact AI browser agents.
-
BrowseSafe-Bench: Security Benchmark for AI Browser Agents
By
–
BrowseSafe-Bench is our security benchmark designed to evaluate the robustness of AI browser agents against prompt injection attacks embedded in realistic HTML environments.
-
Prompt Injection Attacks: Hidden Malicious Instructions for AI Agents
By
–
Prompt injection involves embedding malicious instructions in text read by AI agents, altering its behavior unnoticed. Attackers hide this in comments, templates, footers, or invisible HTML elements parsed by agents but unseen by users.
-
BrowseSafe: Open-Source Model Prevents Malicious Prompt Injections
By
–
Today we're releasing BrowseSafe and BrowseSafe-Bench: an open-source detection model and benchmark to catch and prevent malicious prompt-injection instructions in real-time.
-
AI Avatar Technology Enables Virtual Clothing Try-On Experience
By
–
No more guessing how clothes will look on you.
— Perplexity (@perplexity_ai) 26 novembre 2025
Select a product, click "Try it on," and create your avatar. pic.twitter.com/2G2mYl4XS3No more guessing how clothes will look on you. Select a product, click "Try it on," and create your avatar.