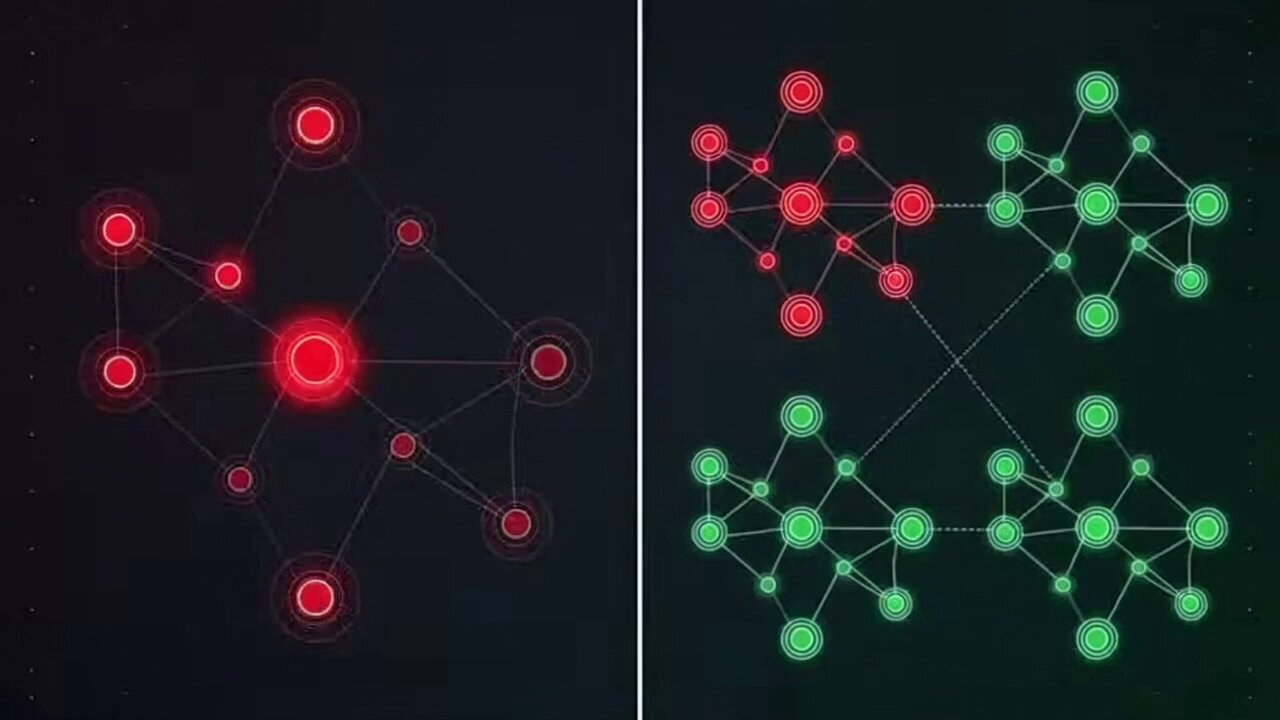
Segmented architecture treats each data source as an isolated domain. Compromised HMIs cannot pivot to historians or control systems because the blast radius stops at segment boundaries.
@fogoros
-
Unified Namespace Security Risk: Single Point of Failure
By
–
Unified Namespace creates a single point of failure for entire manufacturing operations. When one system gets compromised, attackers have immediate access to historical data and control systems.
-
Unified Namespace Security Risks Industrial HMI Compromise
By
–
Under a flat Unified Namespace, a compromised HMI in one building has a direct data path to the corporate historian. Segmented architecture contains that blast radius. See the alternative at #HM26, Stand A12. Partner content with @skkynetinc. #skkynet_ai pic.twitter.com/yuftvBGoLn
— Lucian Fogoros (@fogoros) 15 avril 2026Under a flat Unified Namespace, a compromised HMI in one building has a direct data path to the corporate historian. Segmented architecture contains that blast radius. See the alternative at #HM26, Stand A12. Partner content with @skkynetinc
. #skkynet_ai -
Removable Media Security Policy Gaps and Threat Coverage
By
–
If your removable media policy only mentions USB drives, what percentage of actual threats does it miss?
-
USB Device Security: Expanding Scrutiny Beyond Storage
By
–
Any device that connects to a USB port, including keyboards, diagnostic tools, and personal phones, should fall under the same scrutiny as storage devices.
-
USB Port Security Incident on HMI Device Highlights Default Settings Risk
By
–
The phone charging incident had no malicious intent. The operator needed power, there was an open USB port on an HMI, and the device's default tethering setting did the rest.
-
Beyond USB: Programmable Devices as Security Threats
By
–
Most security talks focus on USB storage. The real threat surface includes programmable keyboards, webcams with payloads, and network adapters. Extend removable media definition beyond flash drives. Partner content with @OPSWAT. #opswat_ics pic.twitter.com/aouQOKzDO9
— Lucian Fogoros (@fogoros) 15 avril 2026Most security talks focus on USB storage. The real threat surface includes programmable keyboards, webcams with payloads, and network adapters. Extend removable media definition beyond flash drives. Partner content with @OPSWAT
. #opswat_ics -
Document of Record Layer Transforms Dark Data for AI Trust
By
–
The solution isn't bigger models or more GPUs. It's creating that document of record layer that transforms dark data into something AI can actually trust.
-
AI Accuracy Fails With Unverified Data and Poor Data Quality
By
–
Most organizations point AI at decades of unverified PDFs and disconnected engineering records, then wonder why accuracy drops through the floor.
-
AI Projects Need Governed Accuracy Layers for Success
By
–
AI projects fail because of missing governed accuracy layers.
— Lucian Fogoros (@fogoros) 15 avril 2026
Raw unstructured content needs transformation into documents of record before AI can reason against them with certainty. Partner content with Adlib. #adlib_iiot pic.twitter.com/q66wW9tJUOAI projects fail because of missing governed accuracy layers.
Raw unstructured content needs transformation into documents of record before AI can reason against them with certainty. Partner content with Adlib. #adlib_iiot