But FHE is not so practical for these models. And it may be infeasible to use some of these large models on a user's device. So even with private fine-tuning, then privacy at inference time still remains. 11/n
SECURITY
-
Privacy in Medical Imaging: AI Generalization Challenges
By
–
Why not? CIFAR-10 style pictures are well-represented in ImageNet, differing primarily in terms of resolution. This may not be the case for settings where we care about privacy, such as medical imaging: by nature of being private, similar pictures are not broadly available. 9/n
-
Privacy in Machine Learning: Scaling Challenges and Solutions
By
–
3. Scale makes ML hard to use in a truly private fashion. If you want to do inference on a point without sharing it, you either have to fine-tune&run the model locally (see e.g. this nice paper by @simran_s_arora @HazyResearch https://
arxiv.org/abs/2205.13722), or use FHE encryption. 10/n -
Private ML Progress Measurement Benchmarks Need Reassessment
By
–
2. We're not measuring progress meaningfully. Many of the benchmarks adopted in private ML come from the non-private setting. For example, pre-training on ImageNet and fine-tuning on CIFAR-10. Good starting point, but may not reflect settings we'd want to use private ML. 8/n
-
ML Privacy Risks: Models Can Leak Secrets from Training Data
By
–
There's more such examples in large pre-training datasets. Since ML models pretrained on them without privacy considerations can be coerced to spit secrets out verbatim (see e.g., https://
arxiv.org/abs/2012.07805 by Carlini et al), this dilutes the meaning of "privacy" for such models 7/n -
Public Data vs Private ML Training Ethics
By
–
1. Publicly available data is not the same as public data. For example, http://
insecam.org has livestreams from videocameras with default passwords. This is publicly available. But it certainly should not be used to train an ML model which purports to be "private." 6/n -
Privacy Challenges in Public Data Pretraining and Fine-tuning
By
–
Seems great, right? Public data is plentiful online, we can just download tons of it, pretrain our models with this public data, and do fine-tuning privately! Privacy is solved! Of course not, and we highlight three (orthogonal) considerations for these settings. 5/n
-
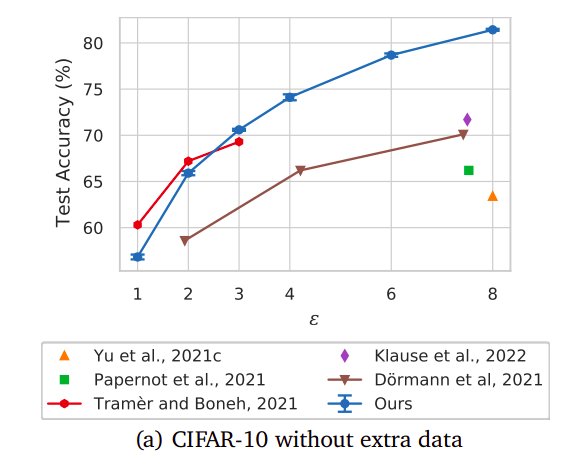
Differential Privacy in ML: CIFAR-10 Performance Gap Challenge
By
–
Differentially private ML is hard. Even basic "solved" tasks in the non-private setting are very hard to do with privacy. Figure from a nice paper by @sohamde_ @LeonardBerrada et al (
https://
arxiv.org/abs/2204.13650), showing SOTA results on CIFAR10.. 60-80%, versus 99%+ non-privately 2/n -

Five Cybersecurity Risk Pillars for All Organization Sizes
By
–
New! #Security For Any Size My #POV – 5 #CyberSecurity Pillars of #Risk https://
bit.ly/SecurityForAll @KingstonTechBiz #Security #IoT #5G #100DaysOfCode @Shi4Tech @Paula_Piccard @ipfconline1 @rafibloom73 #AI @elenacarstoiu #innovation @1DavidClarke #data @michaeldacosta #SME -
Airbus Tests Support Drone Deployed from Bundeswehr A400M
By
–
Airbus drops and pilots a support drone from a Bundeswehr A400M https://actuia.com/actualite/airbus-largue-et-pilote-un-drone-dappui-depuis-un-a400m-de-la-bundeswehr/
… #AI #artificialintelligence #defense
@Airbus